I’ve been continuing with the security focused work on emoncms that I’ve posted about a few times now, E.g Emoncms security notice: read to write apikey privileged escalation vulnerability, please update to emoncms 11.16.8+, Emoncms v11.12.3 stable release - security fixes, Emoncms v11.7.1+.
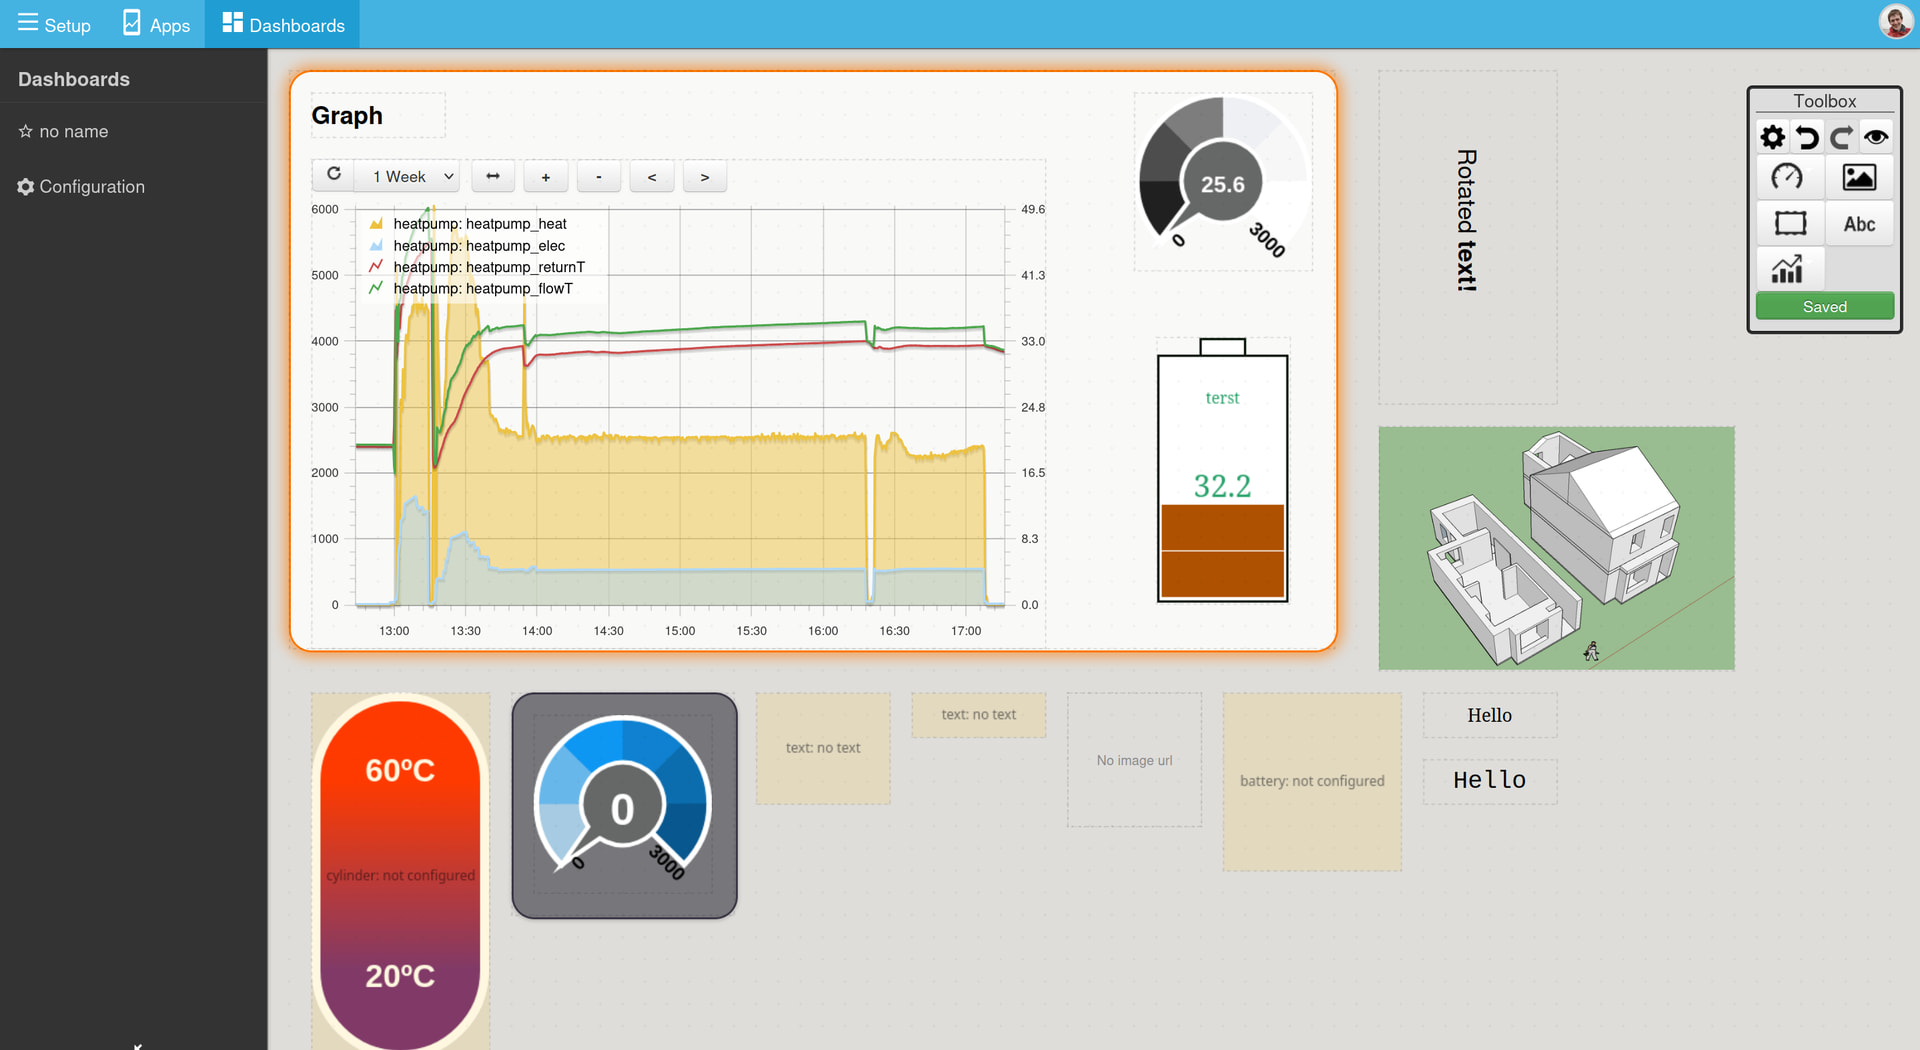
Latest is a fairly substantial security update to the Emoncms dashboard module, mostly focused on reducing the risk of cross site scripting, cross site request forgery and clickjacking attacks, but also fixing a few other things along the way.
We had been using a library called AntiXSS for this but it sat in the repository as a large dependency which was seldomly updated due to php version compatibility issues. Rather than try to list and guard against all possible attacks using AntiXSS the new approach uses a whitelist of specifically allowed dashboard content, this works for emoncms dashboards as dashboards are basically a list of widgets and graphs with known properties - it’s therefore possible to design a conservative whitelist approach, fully under our control, that only lets specific content passed.
This new approach also stores the dashboard data as a JSON object rather than raw HTML and that JSON object is used to re-build and render the dashboards. This is also going to help with future work such as refactoring the way the graphs are integrated in the dashboards (part of my ongoing goal to tidy up the code base).
Visible changes?
For most users there should be no difference. Widgets and charts keep their positions, sizes, options and text. A small number of dashboards will see changes, these are:
- Dashboards using custom style blocks not in-line styles. Custom styles need to be added now as in-line styles.
- Custom iframes inside the dashboards are now removed.
- Links back to emoncms itself are disabled for now until other related work is completed on emoncms core.
Button and curl widgets
Disabled completely on emoncms.org. For local/self-hosted systems these now need to be enabled by adding the following setting to settings.ini:
[dashboard]
enable_action_widgets = true
Other fixes
This update also found and closed the following issues:
- The dashboard editor loaded a dashboard by id alone, so any account could open the content (but not the feed data itself) of somebody else’s private dashboard by asking for its id. It would just show up as blank charts and widgets with NaN values.
- A widget could be given a negative position and sit on top of the emoncms menu bar. Positions are now clamped to the page.
- A widget could be made invisible with zero opacity and still take clicks. Invisible widgets are no longer possible.
- An image could point at an emoncms API call and be fetched with the users session as the page drew. Locally loaded images now need to be placed in
/var/www/emoncms/Modules/dashboard/Views/images. - An image could also leak the dashboard address, and any key in it, to the site it was loaded from. Images are now loaded with no referrer.
- Dashboard names and other fields are now escaped, in the view, the editor and the config dialogue.
How to update
These latest changes are now available in Emoncms core, Dashboard and Graph modules:
- Emoncms core Release 11.18.0 · emoncms/emoncms · GitHub
- Dashboard module Release 3.0.2 · emoncms/dashboard · GitHub
- Graph module Release 3.3.0 · emoncms/graph · GitHub
On a emonHP, emonPi1/2/3, run Admin > Update > Full Update (this will also automatically update the database).
On custom self hosted, update core and modules and then update the SQL database.
Emoncms.org is updated already.
Emoncms core changes
There are also further security improvements to emoncms core in the v11.18.0 release, in particular changing an account email address now requires password verification, this helps reduce the potential for account takeover attacks via CSRF. There’s also new restrictions on which emoncms pages can be placed in a iframe on another site.
Troubleshooting
If you see issues with your dashboard after this change please let me know.

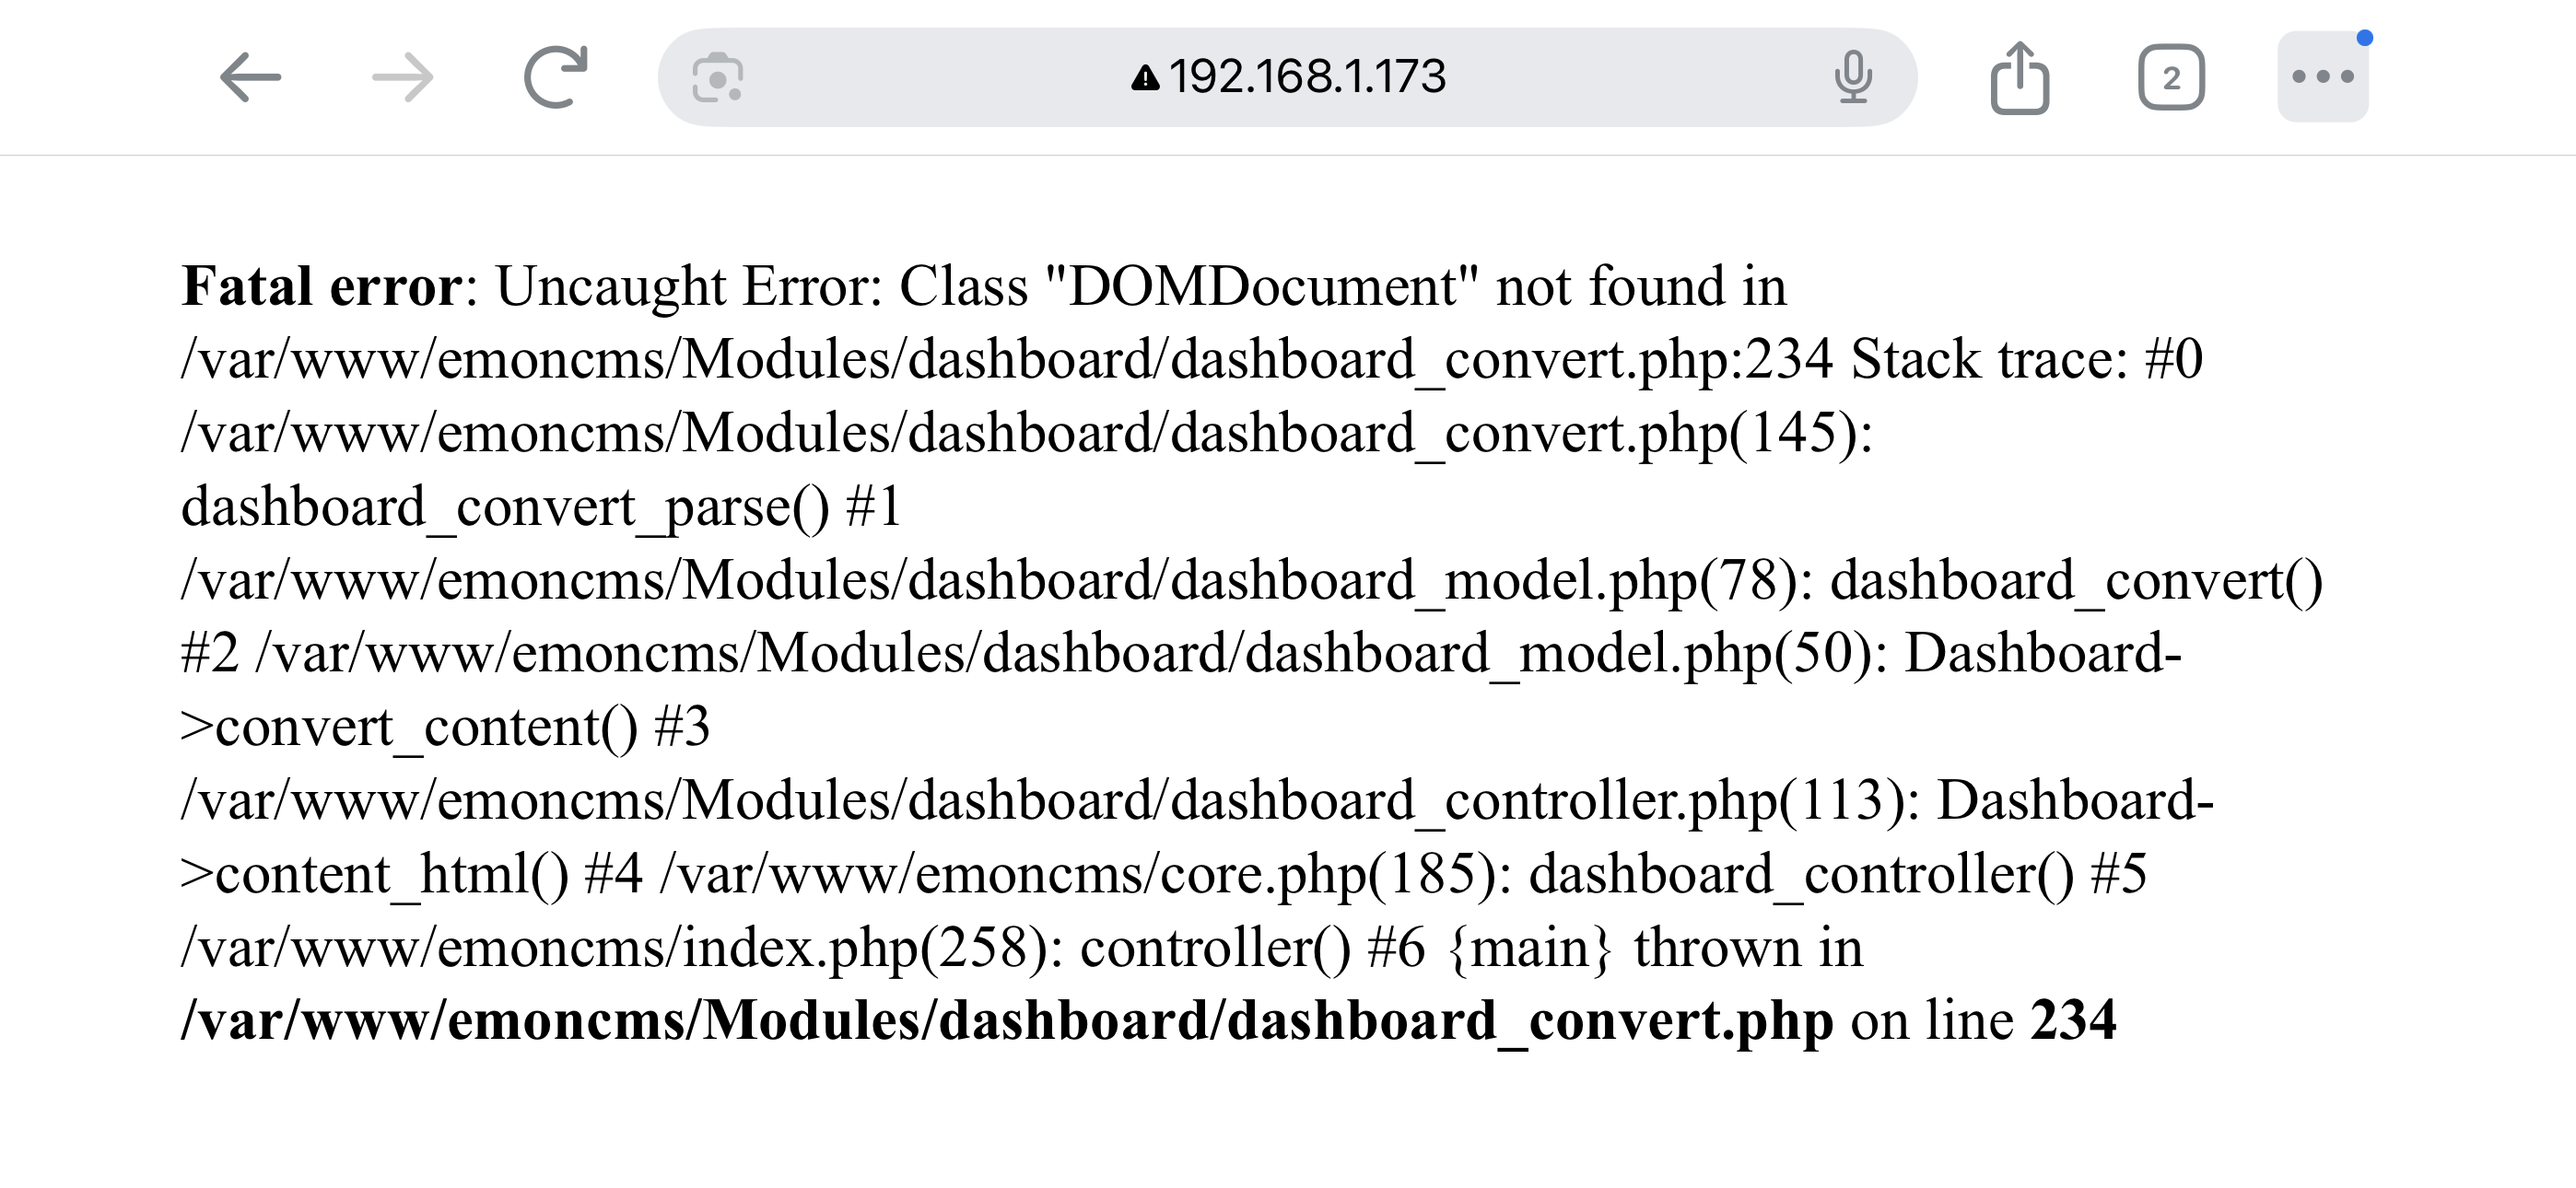
 (need to run update again to get these - v3.1.0).